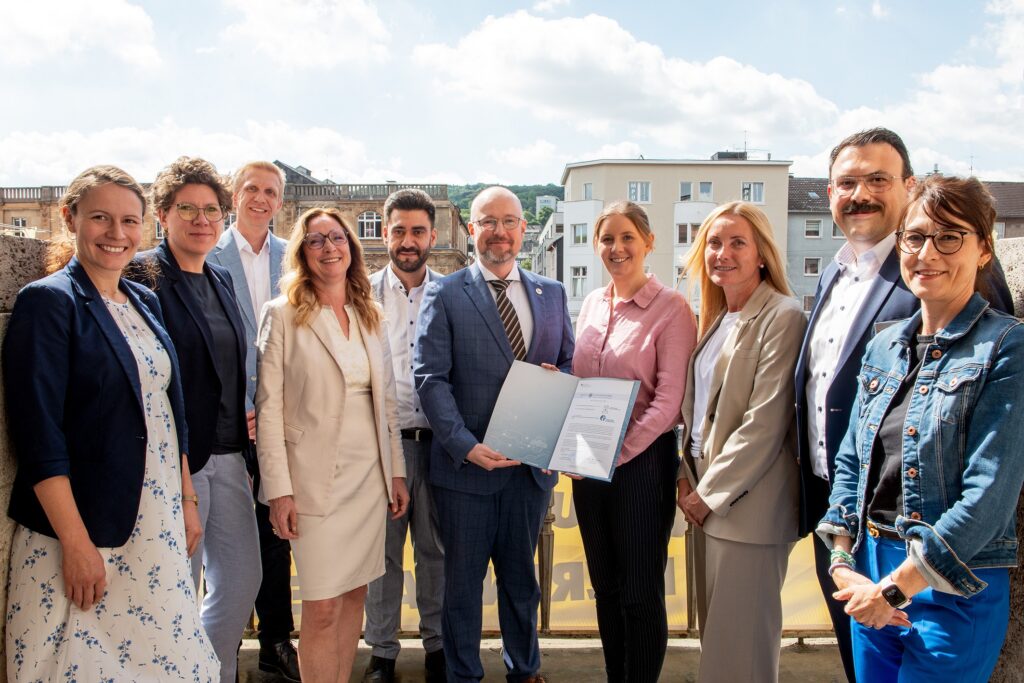
Jana Ehlers and Alexandra Vohlen will continue to help shape the development of international payment security standards during the 2026–2028 term.
SRC Security Research & Consulting GmbH will continue to be represented in the Global Executive Assessor Roundtable (GEAR) of the PCI Security Standards Council (PCI SSC) for the next two years. With the reappointment of Jana Ehlers and Alexandra Vohlen, SRC is a member of this international expert committee for the third consecutive time. Following the appointments for the 2022–2024 and 2024–2026 terms, SRC’s continuous contribution to the development of globally established PCI standards continues.
This reappointment reflects SRC’s long-standing expertise in electronic payment security and confirms the trust that the PCI SSC places in the company’s practical experience and international perspective.
The PCI Security Standards Council – Security standards for global payments
Cashless payments today are global, digital, and highly interconnected. Millions of card payments are processed daily via merchants, payment service providers, banks, data centers, cloud platforms, and payment networks. For these processes to function securely worldwide, uniform security requirements are needed that are understood and implemented by all parties involved.
This task is handled by the PCI Security Standards Council (PCI SSC). The Council was founded in 2006 by the international payment systems American Express, Discover, JCB, Mastercard, and Visa, and has since been developing globally recognized security standards for the protection of cardholder data and payment processes.
The work of the PCI SSC is not limited to publishing technical specifications. The Council develops training and qualification programs for auditors and companies, maintains a continuous dialogue with the international specialist community, and ensures that standards keep pace with technological developments. New payment methods, technologies, and changing threat landscapes are continuously incorporated into the development of the requirements.
Some of the most well-known PCI SSC standards include:
- PCI DSS (Payment Card Industry Data Security Standard) for companies that store, process, or transmit cardholder data,
- PCI PIN Security for the protection of PIN data and cryptographic keys,
- PCI Secure Software and Secure Software Lifecycle for secure payment applications,
- PCI Point-to-Point Encryption (P2PE) for encrypted payment processes,
- as well as numerous other programs and standards for payment terminals, card production, hardware security modules, and other payment components.
Today, these standards form the global foundation for international electronic payment security and are used by companies in almost every country.
The Global Executive Assessor Roundtable – Practical experience for better standards
Through the Global Executive Assessor Roundtable (GEAR), the PCI SSC facilitates a direct exchange with highly experienced assessor companies worldwide. The goal is to incorporate insights from daily audit practice into the further development of standards and programs at an early stage.
GEAR members advise the PCI SSC on matters such as the practical feasibility of new requirements, the development of audit procedures, qualification programs for assessors, and technological developments and their impact on payment security.
It is precisely this link between standardization and practical application that makes the committee so valuable. Security standards must be applicable worldwide—regardless of whether they are implemented by international corporations, financial institutions, cloud providers, or medium-sized companies.
SRC’s international project experience as a foundation
For many years, SRC has been supporting companies from various industries and regions worldwide with PCI audits and security assessments. The experience gained ranges from classic PCI DSS assessments for merchants to complex international projects with diverse regulatory and technical frameworks.
This practical experience feeds directly into the work of GEAR. Challenges identified by auditors together with their clients can be discussed there and introduced as impulses for the further development of the standards. This creates a continuous transfer of knowledge between international audit practice and standardization.
Conversely, SRC’s clients also benefit from this close exchange. Through its committee work, SRC can anticipate developments within the PCI SSC, new interpretations of existing requirements, and international best practices at an early stage, ensuring that consulting and audit projects are future-proof.
Continuity as a commitment
For SRC, being appointed for the third consecutive time is both recognition and a responsibility. Since the founding of the PCI SSC, the company has been involved in Special Interest Groups, task forces, community meetings, and public consultations, thereby continuously contributing to the development of international security standards.
By continuing its work in the Global Executive Assessor Roundtable, SRC maintains this commitment. The goal remains to constructively contribute experience from international audit projects to the work of the PCI SSC and thus help develop secure, practical, and globally applicable standards for electronic payments.